Secrets
On this page
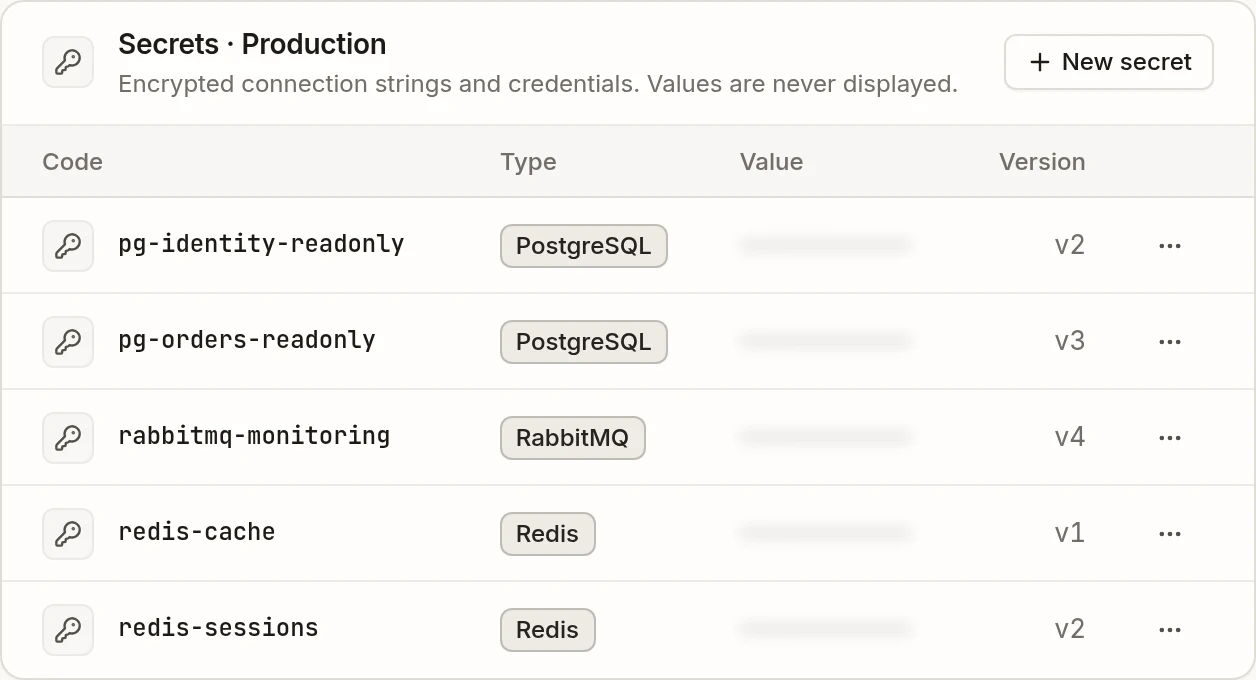
A secret stores a connection string — the address, user and password a sensor needs to reach a database, a Redis store or a RabbitMQ broker. Secrets belong to an environment, are encrypted as soon as they are saved, and are never displayed again: not to you, not to your team.
Secrets require an Enterprise plan and are managed by Managers and Admins.
Which sensors use secrets#
| Secret type | Sensor |
|---|---|
| PostgreSQL, SqlServer, MySQL, MariaDB, Oracle | SQL database |
| Redis | Key-value store |
| RabbitMQ | Dead-letter queue |
Create a secret#
- Open Configuration → Environments and select the environment.
- In the Secrets card, click New secret.
- Fill in:
- Code — lowercase letters, digits, hyphens and dots, unique in the environment, for example
pg-orders-readonly. Sensors refer to the secret by this code. - Type — what it connects to. It cannot be changed afterwards.
- Value — the connection string (examples below).
- Code — lowercase letters, digits, hyphens and dots, unique in the environment, for example
- Save. The value is encrypted at once.
Use a secret in a sensor#
In a SQL, Key-value or Dead-letter queue sensor, the connection section has a Secret selector. It lists the secrets of the sensor's environment with a compatible type, as [Type] code. If none exists, Configure secrets leads to the environment.
Choosing a secret requires the Manager role. A sensor that uses pg-orders-readonly in Staging and the same code in Production connects to two different databases: create the secret with the same code in each environment.
Update and delete#
- Update value stores a new version (
v2,v3…). Sensors use the latest version from their next check. - Delete all versions removes the secret. It is refused while an active sensor of the environment uses it: change or delete that sensor first.
Connection string examples#
Use a dedicated, read-only account: the agent only needs to connect and read.
Server=127.0.0.1;Port=5432;Database=myDataBase;User Id=myUsername;Password=myPassword;Server=myServerAddress;Database=myDataBase;User Id=myUsername;Password=myPassword;Server=127.0.0.1;Port=3306;Database=myDataBase;User Id=myUsername;Password=myPassword;Server=127.0.0.1;Port=3306;Database=myDataBase;User Id=myUsername;Password=myPassword;Data Source=myOracleDB;User Id=myUsername;Password=myPassword;redis0:6380,password=myPassword,ssl=True,abortConnect=Falseamqp://user:password@host:port/vhostHow secrets are protected#
Secrets are encrypted with a key unique to your organization, and only decrypted when a check needs them, to be sent to the agent that runs it over its encrypted connection. See Secret security.