Certificate validity
The Certificate validity sensor connects to a host over TLS, reads its certificate and checks how many days remain before it expires. Use it so that no certificate ever expires unnoticed — on your websites, your APIs or your partners' endpoints.
In the wizard: SSL certificate.
Settings#
| Setting | Description |
|---|---|
| Host | The host whose certificate to read, for example edi.partner.example. |
| Alert before expiry | Number of days before expiry at which the check fails, from 1 to 730. |
The check always runs once a day.
When is it healthy?#
When the certificate expires in more days than Alert before expiry. The sensor watches the expiry date; to fail on any certificate error (wrong name, untrusted chain), add an HTTP sensor with Verify SSL certificate on.
The days remaining#
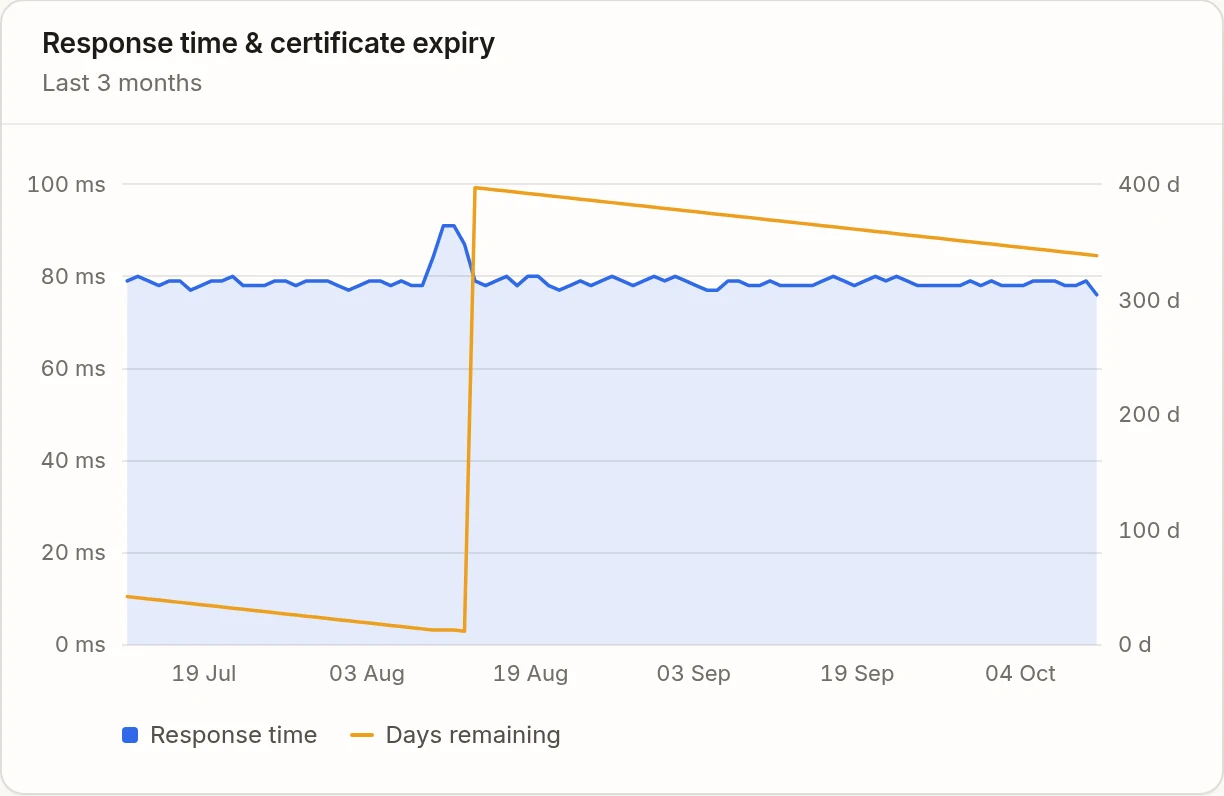
The number of days before expiry is recorded with every check and charted: it decreases day after day, then jumps back up when the certificate is renewed.
Example#
Partner EDI — TLS certificate: host edi.partner.example, alert 14 days before expiry, severity Major. The incident opens two weeks before the deadline and is resolved by itself once the partner renews.
Good to know#
The sensor connects on port 443.